Most teams still talk about the EU AI Act as if there is plenty of time left. There is not. Enterprise leaders need to know exactly what must be in place before enforcement starts, and whether it already is.
This article gives a practical readiness checklist that legal, product, engineering and operations can work from together.
Key message: AI compliance is a production architecture exercise, much more than a document exercise.
Many companies made one strategic mistake. They put compliance in legal review and left it out of operational design. Three outcomes follow from that almost every time: controls exist only on paper, decision trails are incomplete, and AI deployment scales faster than the risk controls around it. If this sounds familiar, you are not alone, and it can still be fixed in a short time if the focus is on execution.
The first item is an inventory. List every AI use case you have, including the pilots and the tools that are still in procurement, and keep that list current; a spreadsheet filled in once for a steering committee does not count. Per use case you write down the purpose, the owner, which categories of data it touches, what harm a wrong output could do and how the Act will probably classify it, high risk or not. You cannot control what you have not listed. Our library of AI use cases by industry and function is a useful reference while you build it.
Second, accountability. Somebody with real authority has to own each AI system. If three teams share it vaguely, an incident turns into a discussion about whose problem it is. We suggest one named owner for the quality of outcomes, one for technical controls and reliability, and one for regulatory alignment.
Logging and traceability should be on by default. For any critical AI decision you need to be able to reconstruct the whole path, from the input context and the model version to the tool calls, the approvals and the final action. A decision you cannot replay is a decision you cannot defend.
Where the impact is high, add human oversight. Keeping a human in the loop is a risk control, and a perfectly modern one. Use approval gates for actions such as pricing, legal interpretation, compliance recommendations and financial instructions.
Data governance deserves its own check, since most AI errors turn out to be data errors. Training data, retrieval data and tool data should be relevant, current, correctly permissioned and versioned so that an auditor can see what was used when.
Technical documentation has to be something your teams will maintain. A one time PDF goes stale within a release or two. Generate documentation from the delivery workflow and update it with each release, covering assumptions about model behavior, guardrails, known limits, fallback paths and escalation flows.
Testing should cover accuracy, robustness and abuse. Benchmark screenshots are not evidence. Run structured evaluations with adversarial prompts, boundary requests, tool failures and edge cases in specific regions and languages, all taken from real workflows.
Finally, if a use case falls under the high risk obligations, prepare registration, conformity checks and continuous monitoring early. Leaving this until procurement or launch week is expensive.
Minimal readiness artifact set:
- AI use-case register with risk tier
- Control ownership matrix
- Decision trace logging specification
- Evaluation suite with pass/fail gates
- Remediation backlog with deadlines
To build momentum, we suggest working in weekly steps. In week 1 the focus is inventory and risk classification. Week 2 settles ownership and the design of the controls. In week 3, logging, oversight and evaluations go into operation. Week 4 closes the loop with documentation, a governance review and a remediation backlog.
"Compliance velocity comes from operational clarity, not from larger policy documents."
Perfect governance in 30 days is not the goal. What you want after a month is control that is real, visible and able to scale.
The teams that do well in enterprise AI will not be the ones with the most demos. They will be the ones that can show they are in control while still shipping at speed. In 2026, compliance is a condition for innovation that lasts.
I think it's great that technology is so embedded in our daily lives. It helps us get knowledge faster, finish tasks more efficiently, gives us inspiration, and occasionally scares the hell out of us with those crazy (fake) videos. I help a lot of companies implement AI, so in the end it pays my bills. But after spending a ridiculous amount of time with all these new technologies, it's time to write down the things I really hate about AI.
Read More →
AI Technology06-10-2026
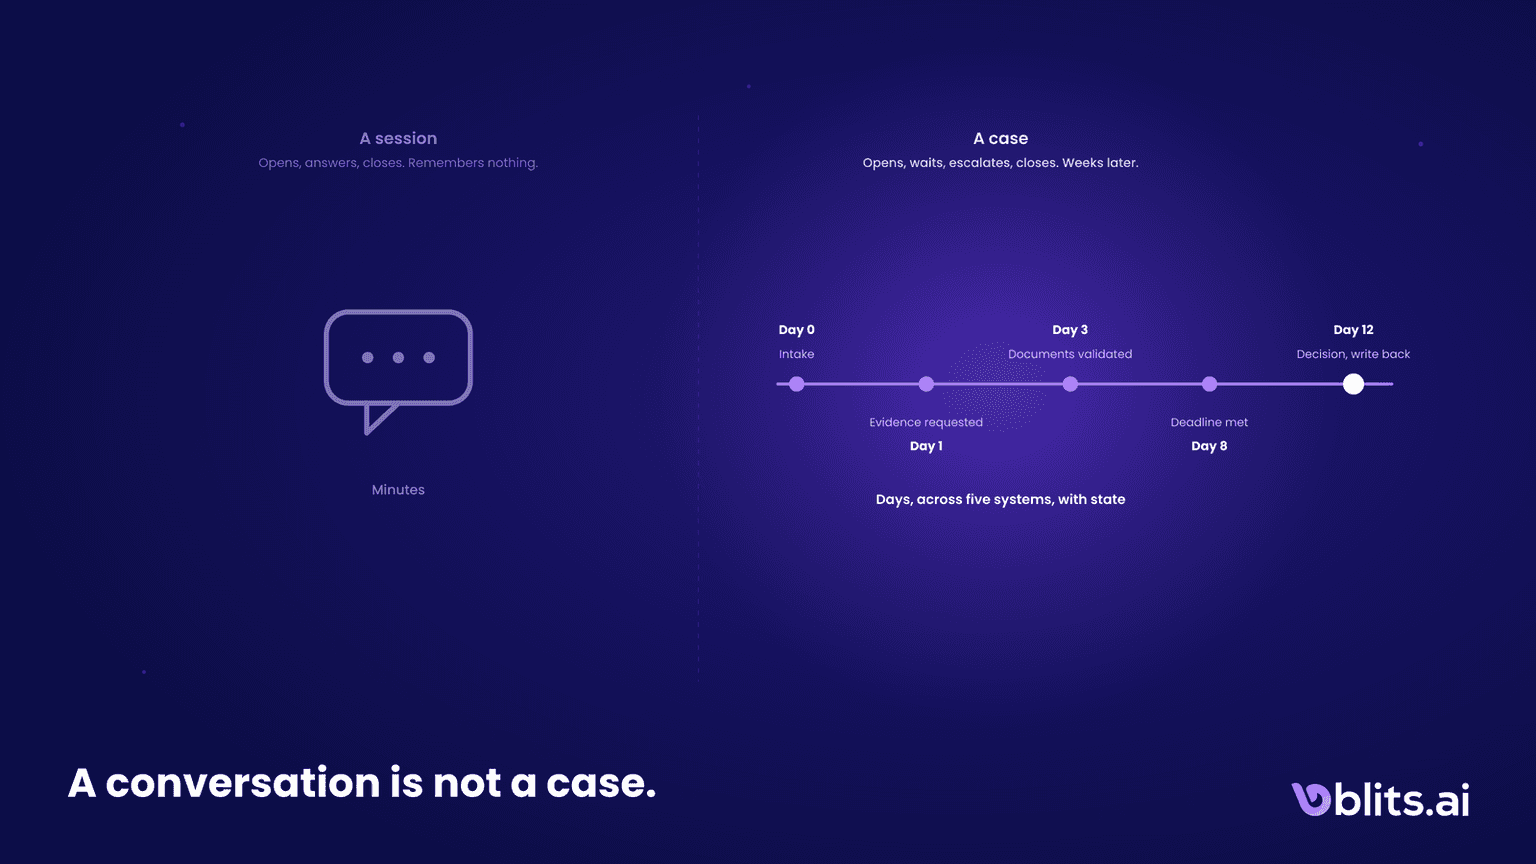
A Conversation Is Not a Case
The 95 percent pilot failure stat is making the rounds again, this time with a diagnosis I actually agree with: chatbots automate sessions, but a bank runs cases. Why the unit of work decides whether your AI survives production, and the day eight test that shows which one you built.
Read More →
AI Technology10-04-2026
Agentic AI Languages and Dialects: Why Voice Quality Is Still the Hard Part
Agentic systems promise autonomous workflows, but speech and dialect quality fail first. Why Arabic, Turkish, Chinese and more run into the same gap.
Read More →
Stay Updated
New posts on conversational AI, enterprise automation and customer experience, sent to your inbox when they go live